One Budget, One Team, One Set of Risks
A technology leader's blueprint for transforming enterprise operations through strategic modernization, unified data governance, r…
Read the article
FOUNDER TO THE PROFILE
Executive Vice President of IT and Security, arrivia
“Technology and security were never two jobs. They’re one budget, one team, and one set of risks — and the moment you run them that way, the trade-offs stop being arguments and start being decisions.”
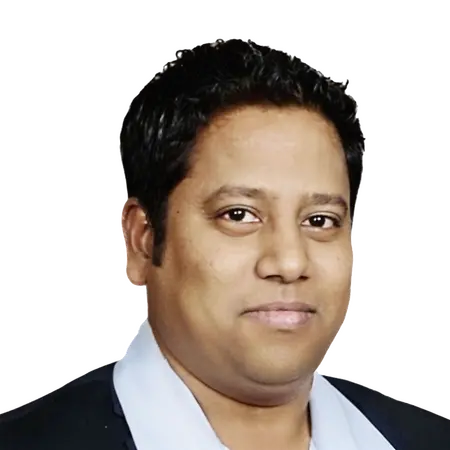
Benito Ralph is a technology and security executive who leads the enterprise IT, data, artificial intelligence, and cybersecurity functions as a single, converged mandate. He owns the technology and security roadmap end to end and leads a global organization of more than 100 engineers, architects, analysts, and operators across cloud, application, infrastructure, and security disciplines, running a 24x7x365 operation that supports every booking, member, and supplier interaction the business depends on. Benito manages technology and security as one $12M portfolio rather than as competing cost centers. Through platform modernization, resource optimization, and renegotiated vendor agreements, he has reduced expenses by 25% and delivers $1M in recurring annual savings, while establishing enterprise AI consumption as a managed budget line with usage-based cost controls.
Cloud transformation and reliability. Benito led the migration of 65% of on-premises services to cloud and hyper-converged platforms, cutting total cost of ownership by 55% and generating $2.2M in annual savings. Over the same period he raised system availability from 94% to 99.99% and improved operational efficiency by 20% through AIOps-driven anomaly detection, predictive capacity management, and automation of routine remediation. He designed and built the organization’s unified data foundation, combining an eventhouse, a lakehouse, and streaming ingestion to consolidate more than 100 source systems across booking, member, and supplier domains into a single governed layer. The platform reduced report build time by 40%, retired redundant data marts, and standardized semantic definitions so that finance, marketing, and operations report from one shared set of numbers.
AI operating model and applied AI. Benito established the enterprise AI operating model, including a use-case intake and triage process and an AI management system. The framework provides business units with a documented path from idea to production, supported by a maintained model and agent inventory, risk tiering, human-in-the-loop requirements, and evaluation gates that every workflow must clear. Under this model, AI has been deployed to service-desk triage and resolution, product-defect detection, and supply-chain and travel-logistics optimization on a multi-model architecture that avoids vendor lock-in. Each use case is funded against a defined P&L payback and tracked after launch, delivered through SRE, DevOps, and AI-first engineering practices.
Security program leadership. Benito built the enterprise security program from the ground up, taking the company from no certifications to PCI DSS 4.0, SOC 2 Type I and Type II, and sustaining each through annual audits. He has repositioned compliance from a cost center to a contract prerequisite that unblocks enterprise deals. He implemented zero-trust controls on Microsoft Entra ID, including multi-factor authentication, conditional access, and privileged access management, establishing least privilege as the default posture across the estate. He directs 24x7 detection and response on Microsoft Sentinel and Defender with AI-assisted triage, continuous vulnerability management, and independent penetration testing, supported by GDPR- and HIPAA-aligned frameworks, disaster recovery, and incident-response readiness. Ralph presents risk posture to executive leadership and the board in business-impact terms, owns the company’s cyber-insurance strategy, and governs third-party risk across payment processors, travel-supplier integrations, and SaaS partners.
Benito’s leadership philosophy centers on accountability for the whole outcome, transparency with boards and teams alike, and the conviction that technology, data, AI, and security deliver the most value when they are owned, funded, and governed together.
IN HIS OWN WORDS
The team, first. A hundred-plus people across cloud, applications, infrastructure, and security, in time zones that never all sleep at once. Nothing in this story was done by me; it was done by people who were willing to run a migration at 2 a.m. or sit through a third audit because they understood why it mattered. My job was to make sure they always knew why.
Second, a refusal to separate things that belong together. Technology and security. Data and the people who argue about it. AI and the budget that pays for it. Every time I’ve pulled two things into one accountable owner, the friction disappeared and the results showed up. Every time I’ve seen them kept apart, the organization spent its energy on handoffs.
Third, speaking the language of the people who fund the work. I learned to translate availability into revenue protected, compliance into deals closed, and risk into dollars at stake. Once the board and the CFO could see technology in their own terms, they stopped treating it as overhead and started treating it as leverage. That shift in how the work was understood did more for my career than any single project.
And some luck, which I’ll admit to. I joined at a moment when the company had everything to build and the appetite to build it. The best I can say is that when the moment came, the team and I were ready for it.
Early on, a mentor told me: solve the problem the business actually has, not the one your job title says you own. It sounded obvious. It took me years to understand how rarely people do it.
Most of us are handed a function and a budget and we optimize inside the lines. The advice was to look up from the lines and ask what the company is really trying to do this year, then make your function the thing that gets it there. For me that meant treating security certifications as a way to close enterprise deals instead of a checklist. It meant treating the data platform as a way to end an argument instead of a technical project. It meant treating AI as a budget line with a payback instead of a lab.
The side effect is that people start handing you bigger problems, because you’ve shown you’ll solve the real one. That’s how a technology role turned into a technology-and-security role, and how one portfolio became the whole roadmap. I didn’t ask for the scope. I asked what the business needed, and the scope followed.
Learn the business before you learn the next tool. The tools will change under you; I’ve watched three generations of cloud platforms and I’m now on my second generation of AI models. What doesn’t change is how a company makes money, where it loses it, and what keeps the people running it awake at night. The engineers who understand that are the ones who get asked into the room where decisions are made.
Take the unglamorous job. Nobody fights over the on-call rotation, the ERP integration, or the audit prep. Those are exactly the places where you learn how the whole system actually works, and where you become the person others can’t run without. Every senior leader I respect spent years doing the work nobody else wanted.
Treat security as part of your craft, not someone else’s department. If you build something, you own whether it can be broken. Developers who think that way are rare, and they move up fast.
And be the person who stays calm. In operations and security, the bad day is coming; the only question is who the team looks to when it arrives. You earn that by being steady on the small days. Credibility in this industry is built in increments and spent all at once, so protect it.
The biggest opportunity and the biggest challenge are the same thing: AI is now cheap enough that everyone in the company can use it and powerful enough that it matters when they do. A year ago the question was whether to adopt it. Now the question is how to govern it without smothering it. Companies that get the operating model right will compound; companies that either ban it or let it sprawl will spend the next five years cleaning up.
Close behind that is cost. Cloud taught us that consumption pricing rewards discipline and punishes everyone else, and AI is cloud all over again, except the meter runs faster. If you don’t treat AI spend as a managed budget line with usage controls, it will show up as a surprise on the P&L, and the first reaction will be to shut it off.
On the security side, the perimeter has dissolved into a web of partners. Payment processors, supplier integrations, SaaS vendors, and now AI providers all sit inside your trust boundary whether you like it or not. Third-party risk used to be a questionnaire; it’s now a core discipline. At the same time, attackers have the same AI tools we do, so the gap between a phishing campaign and a convincing one has closed.
And there’s the data question underneath all of it. AI is only as good as the data you point it at, and most companies still have five versions of the truth. The unglamorous work of building one governed data layer is the thing that turns AI from a demo into a capability. That’s where I’d tell any peer to put their next dollar.
Accountability, and I mean the kind where there’s one name next to the outcome. I’ve structured my whole career around owning the full problem rather than a slice of it, because a slice is where excuses live. If availability drops or an audit fails, I don’t want to be in a meeting where four people explain why it wasn’t their part. That’s true at home too. If I said I’d be there, I’m there.
Transparency. The board gets the real risk picture, in plain terms, even when it’s uncomfortable. The team gets the real reason behind a decision, even when it’s budget. People can handle hard truths; what they can’t handle is finding out later that you softened one. Trust is the only thing that makes a 24x7 operation work, and you can’t build it on a filtered version of events.
Calm. Security and operations are fields where panic is contagious and so is composure. I try to be the steady point in the room on the worst day, and I’ve learned that starts with being steady on ordinary ones. My family would tell you that’s a work in progress.
And stewardship. The systems, the data, the people, the money: none of it is mine. I’m responsible for leaving each of them better than I found them and for handing them to whoever comes next in a state I’d be proud of. That’s the measure I hold myself to, in the office and out of it.
PERSPECTIVES
Original insights, ideas, and viewpoints shaped by real-world experience.
View All ArticlesLEARN MORE
Notable Men brings together influential voices across industries to share insights, experiences, and perspectives that matter.
Learn More